The problem
A lot of WordPress malware no longer sits in a file you can spot by name. It is a few lines of script injected into your pages, a post, an option or a must-use plugin, and it often shows its payload only to visitors.
One version reads its next stage from a public blockchain with a read-only eth_call, so there is no bad domain to block. Guardio Labs named this EtherHiding in their report of 13 October 2023 (checked 20 October 2026).
The payload is often a fake “Verify you are human” box that tells the visitor to paste a command into the Windows Run dialog. Microsoft calls this ClickFix in its analysis of 21 August 2025 (checked 20 October 2026). If your visitors report that page, our guide to the fake Cloudflare check on WordPress shows where the loader hides.
Google’s threat team counted about 14,000 web pages carrying one group’s injected loader by June 2025, placed in plugin files, theme files or the database (Google Threat Intelligence, 17 October 2025, checked 20 October 2026).
We wrote Security Guard after that kind of infection hit a production WordPress site. It runs on your own site, shows you what it found and what it did, and never uploads your files.
How it works
Install the plugin, then activate your licence so the site receives updates. Every feature works without the key. Installing an add-on and activating your licence has the steps.
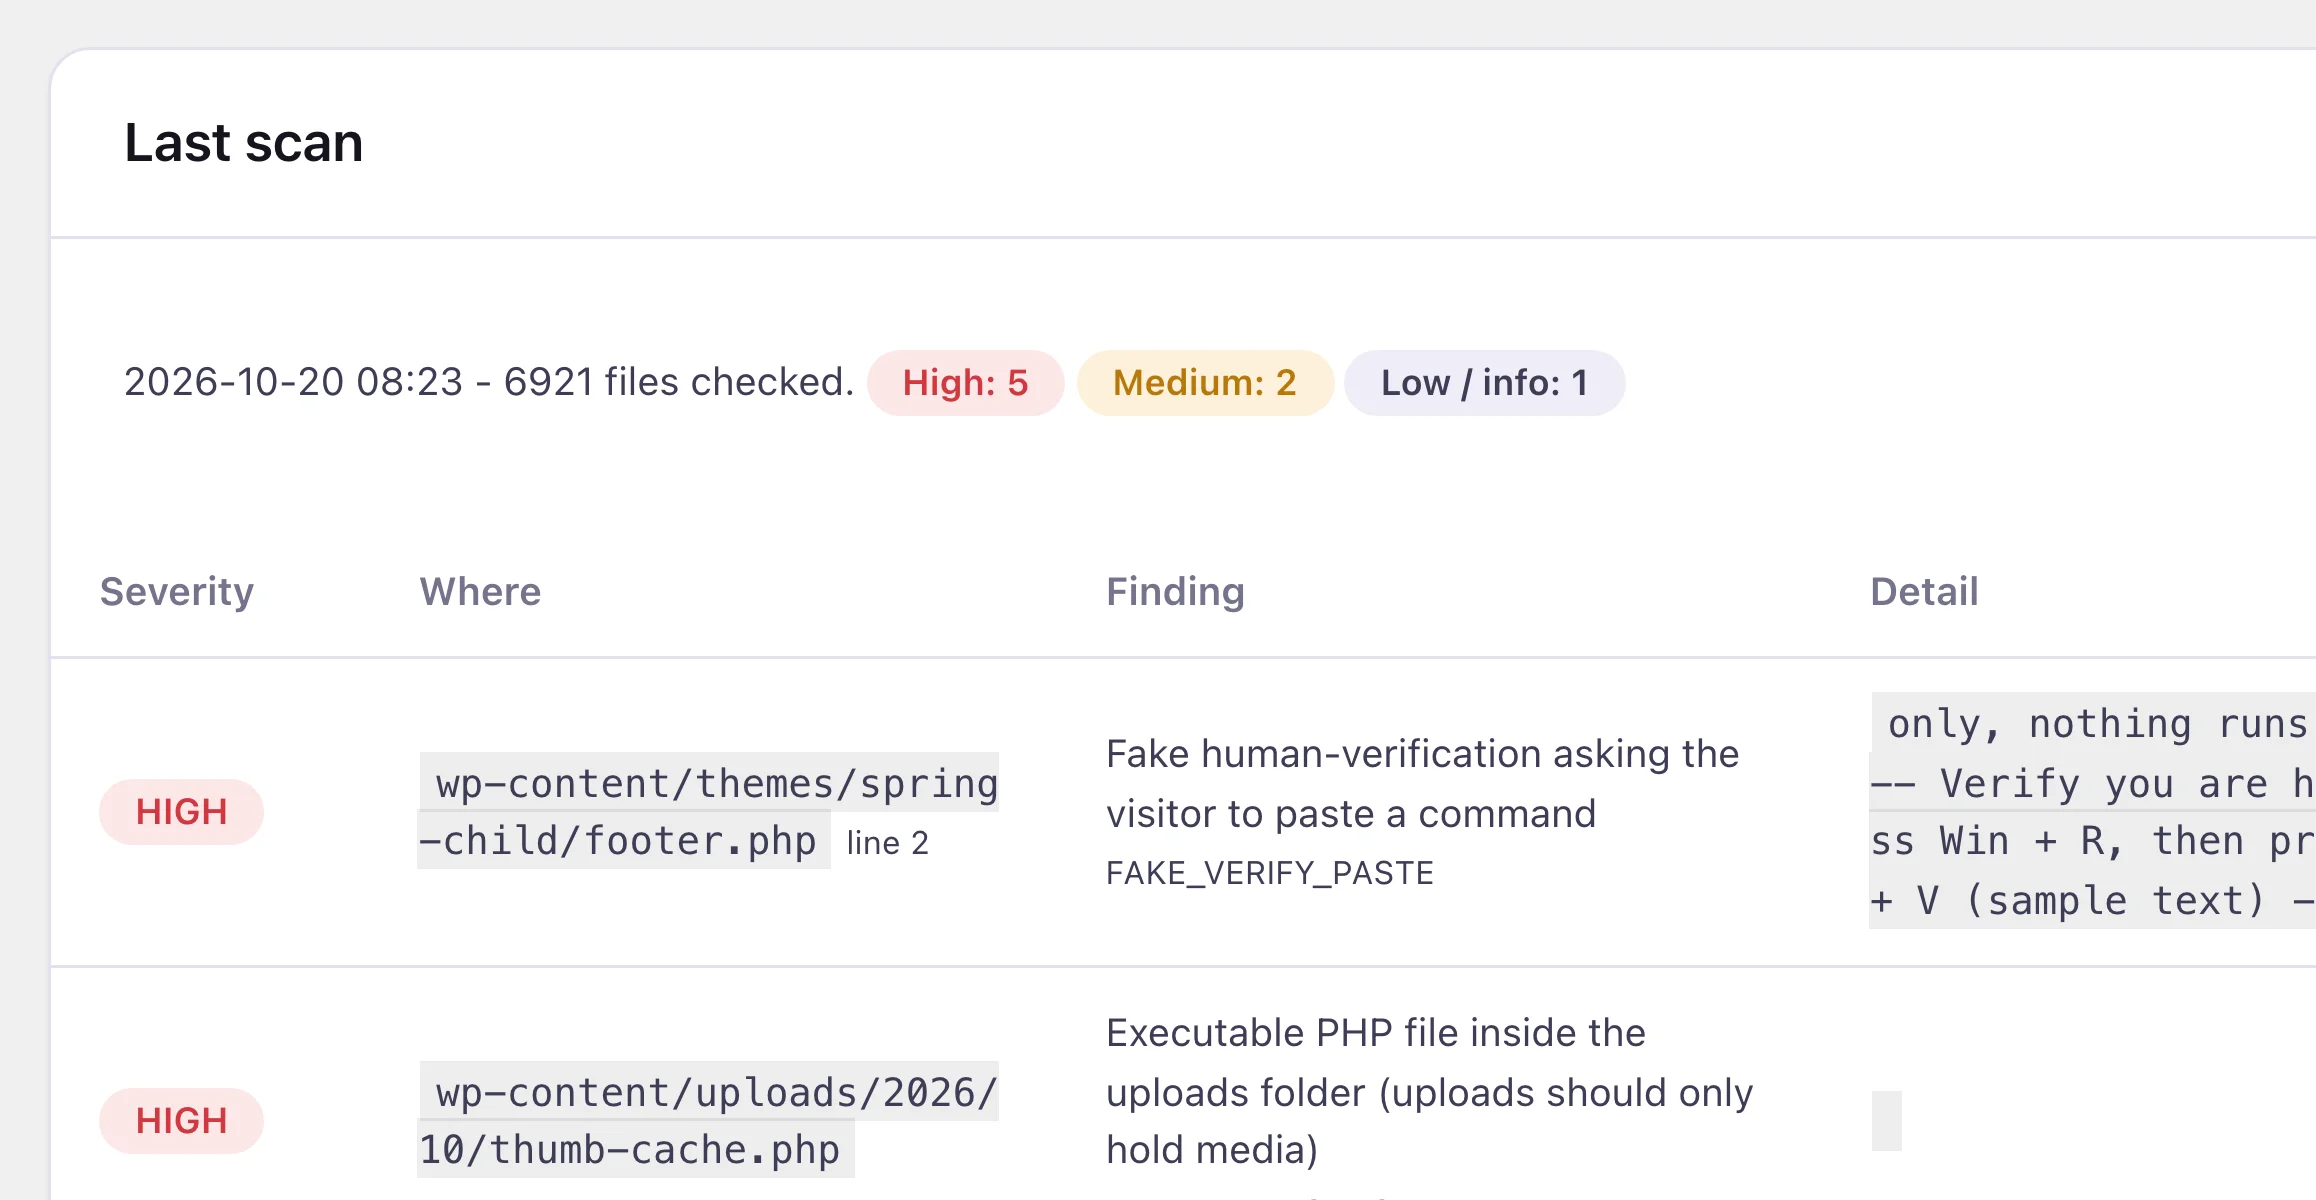
- Run a scan. Settings > Security Guard > Scan checks your plugin, theme and must-use code, the uploads folder, the database, administrator accounts and WordPress core files. It works in short steps, one request at a time, so it doesn’t hit a time limit on slow hosting.
- Read the findings. Each one is High, Medium, Low or Info and says where it is: a file and line, a post, an option or a user. Ignore hides anything you have checked. Once you have cleaned something up, it no longer comes back on the next scan.
- Save a baseline on the Baseline tab once the site is clean. Later scans then flag any code file that was added or changed, any new must-use plugin and any new administrator.
- Turn on the protection. On the Protection tab, Remove injected scripts takes known loader scripts out of your pages before they reach the visitor. The Content-Security-Policy starts in Report only mode, so nothing breaks while you read the log. Switch it to Enforce and page scripts can no longer call hosts you haven’t allowed.
On 20 October 2026 we planted an EtherHiding-style loader and a ClickFix clipboard script on a test site. With Remove injected scripts on, both came out of the page and each left a High line in the event log, while the theme’s own scripts stayed. On our development Mac the filter checked a page with 20 ordinary inline scripts in well under a millisecond and left it unchanged.
Scan data stays on your server, in a private folder with a random name and deny rules for Apache, LiteSpeed and IIS. The scan files hold no administrator e-mail addresses.
Keeping track
The event log keeps the newest 200 events. It records new administrators, promotions to administrator, plugins activated or deactivated, theme switches and administrator logins. It also logs 10 failed logins in 10 minutes from one IP address, new must-use plugins, removed scripts and scan results.
Content-Security-Policy violations go into the log quietly, without e-mails, and repeats are capped so a busy page can’t flood it. If the script filter can’t check a page, it logs that instead of skipping it silently.
A scan runs by itself every day. E-mail alerts for medium and high events are there, but off until you turn them on. Developers can run wp security-guard scan from the command line: it exits with code 1 when it finds anything High, so a deploy script can stop.
The Security Guard user guide covers every setting, and has a clean-up checklist for when the scan finds something. For the checks you can run by hand, without any plugin, read how to check if your WordPress site is hacked.
What it doesn’t do
- It is not a firewall. It does not stop an attack before it reaches WordPress. It finds and contains what it can see on the site.
- It does not delete or repair anything it flags. You get a report and decide, so it cannot break your site by removing the wrong file.
- It has no two-factor login, login limiting or vulnerability database in this version. Our comparison of WordPress malware scanners shows which tools add those.
- It finds known patterns. A new, differently written loader may not match until the signature list is updated, which is what the baseline is for.
- It can’t see an administrator hidden by a
pre_user_query filter, because it asks WordPress for the user list. If the code that hides it arrived after you saved a baseline, the scan flags that file as added or changed. - The Content-Security-Policy still allows inline scripts, so themes and page builders keep working. Its job is to stop page scripts calling hosts you haven’t allowed. Removing injected inline scripts is the filter’s job.
- Scan time depends on your host: about six minutes for 11,516 files on our development machine.
- Blocking PHP in uploads is an .htaccess rule for Apache and LiteSpeed. On Nginx you add your own rule. Nginx and multisite have not been tested yet.